| Identity and access |
| Single sign-on | Entra ID, Auth0, SiteMinder or any OIDC or SAML 2.0 IdP, or a trusted SiteMinder-style header. necodoc creates the account at first sign-in. | Single sign-on |
| Role mapping | IdP groups map to roles: admin, publisher, reviewer, editor, viewer. A user can hold several roles, and each role grants one kind of work. | Users and roles |
| Session control | Admins ban users, revoke sessions and reset passwords. Impersonation is admin-only and audited from start to stop. | Users and roles |
| System access |
| Service accounts | Keys belong to a person or to a service account that can never sign in. | ADR 0029 |
| Scoped keys | Each key has scopes no wider than its owner's roles, an optional template allowlist, IP allowlist and expiry date, and a rate limit. Admins can revoke a key and see its usage. | HTML to PDF API |
| Signed callbacks | Webhooks carry an HMAC-SHA256 signature over the timestamp and body. necodoc logs each delivery attempt. | Webhooks |
| Data |
| Residency | Records in your Postgres; PDFs in your S3-compatible bucket, Azure Blob container or disk, in the region you choose. | ADR 0023 |
| Downloads | Files download through signed links that expire. The audit log records each link that is issued. | Generation log |
| Retention | An admin sets how long generated PDFs, and optionally their input data, are kept. | Generation log |
| Audit and logging |
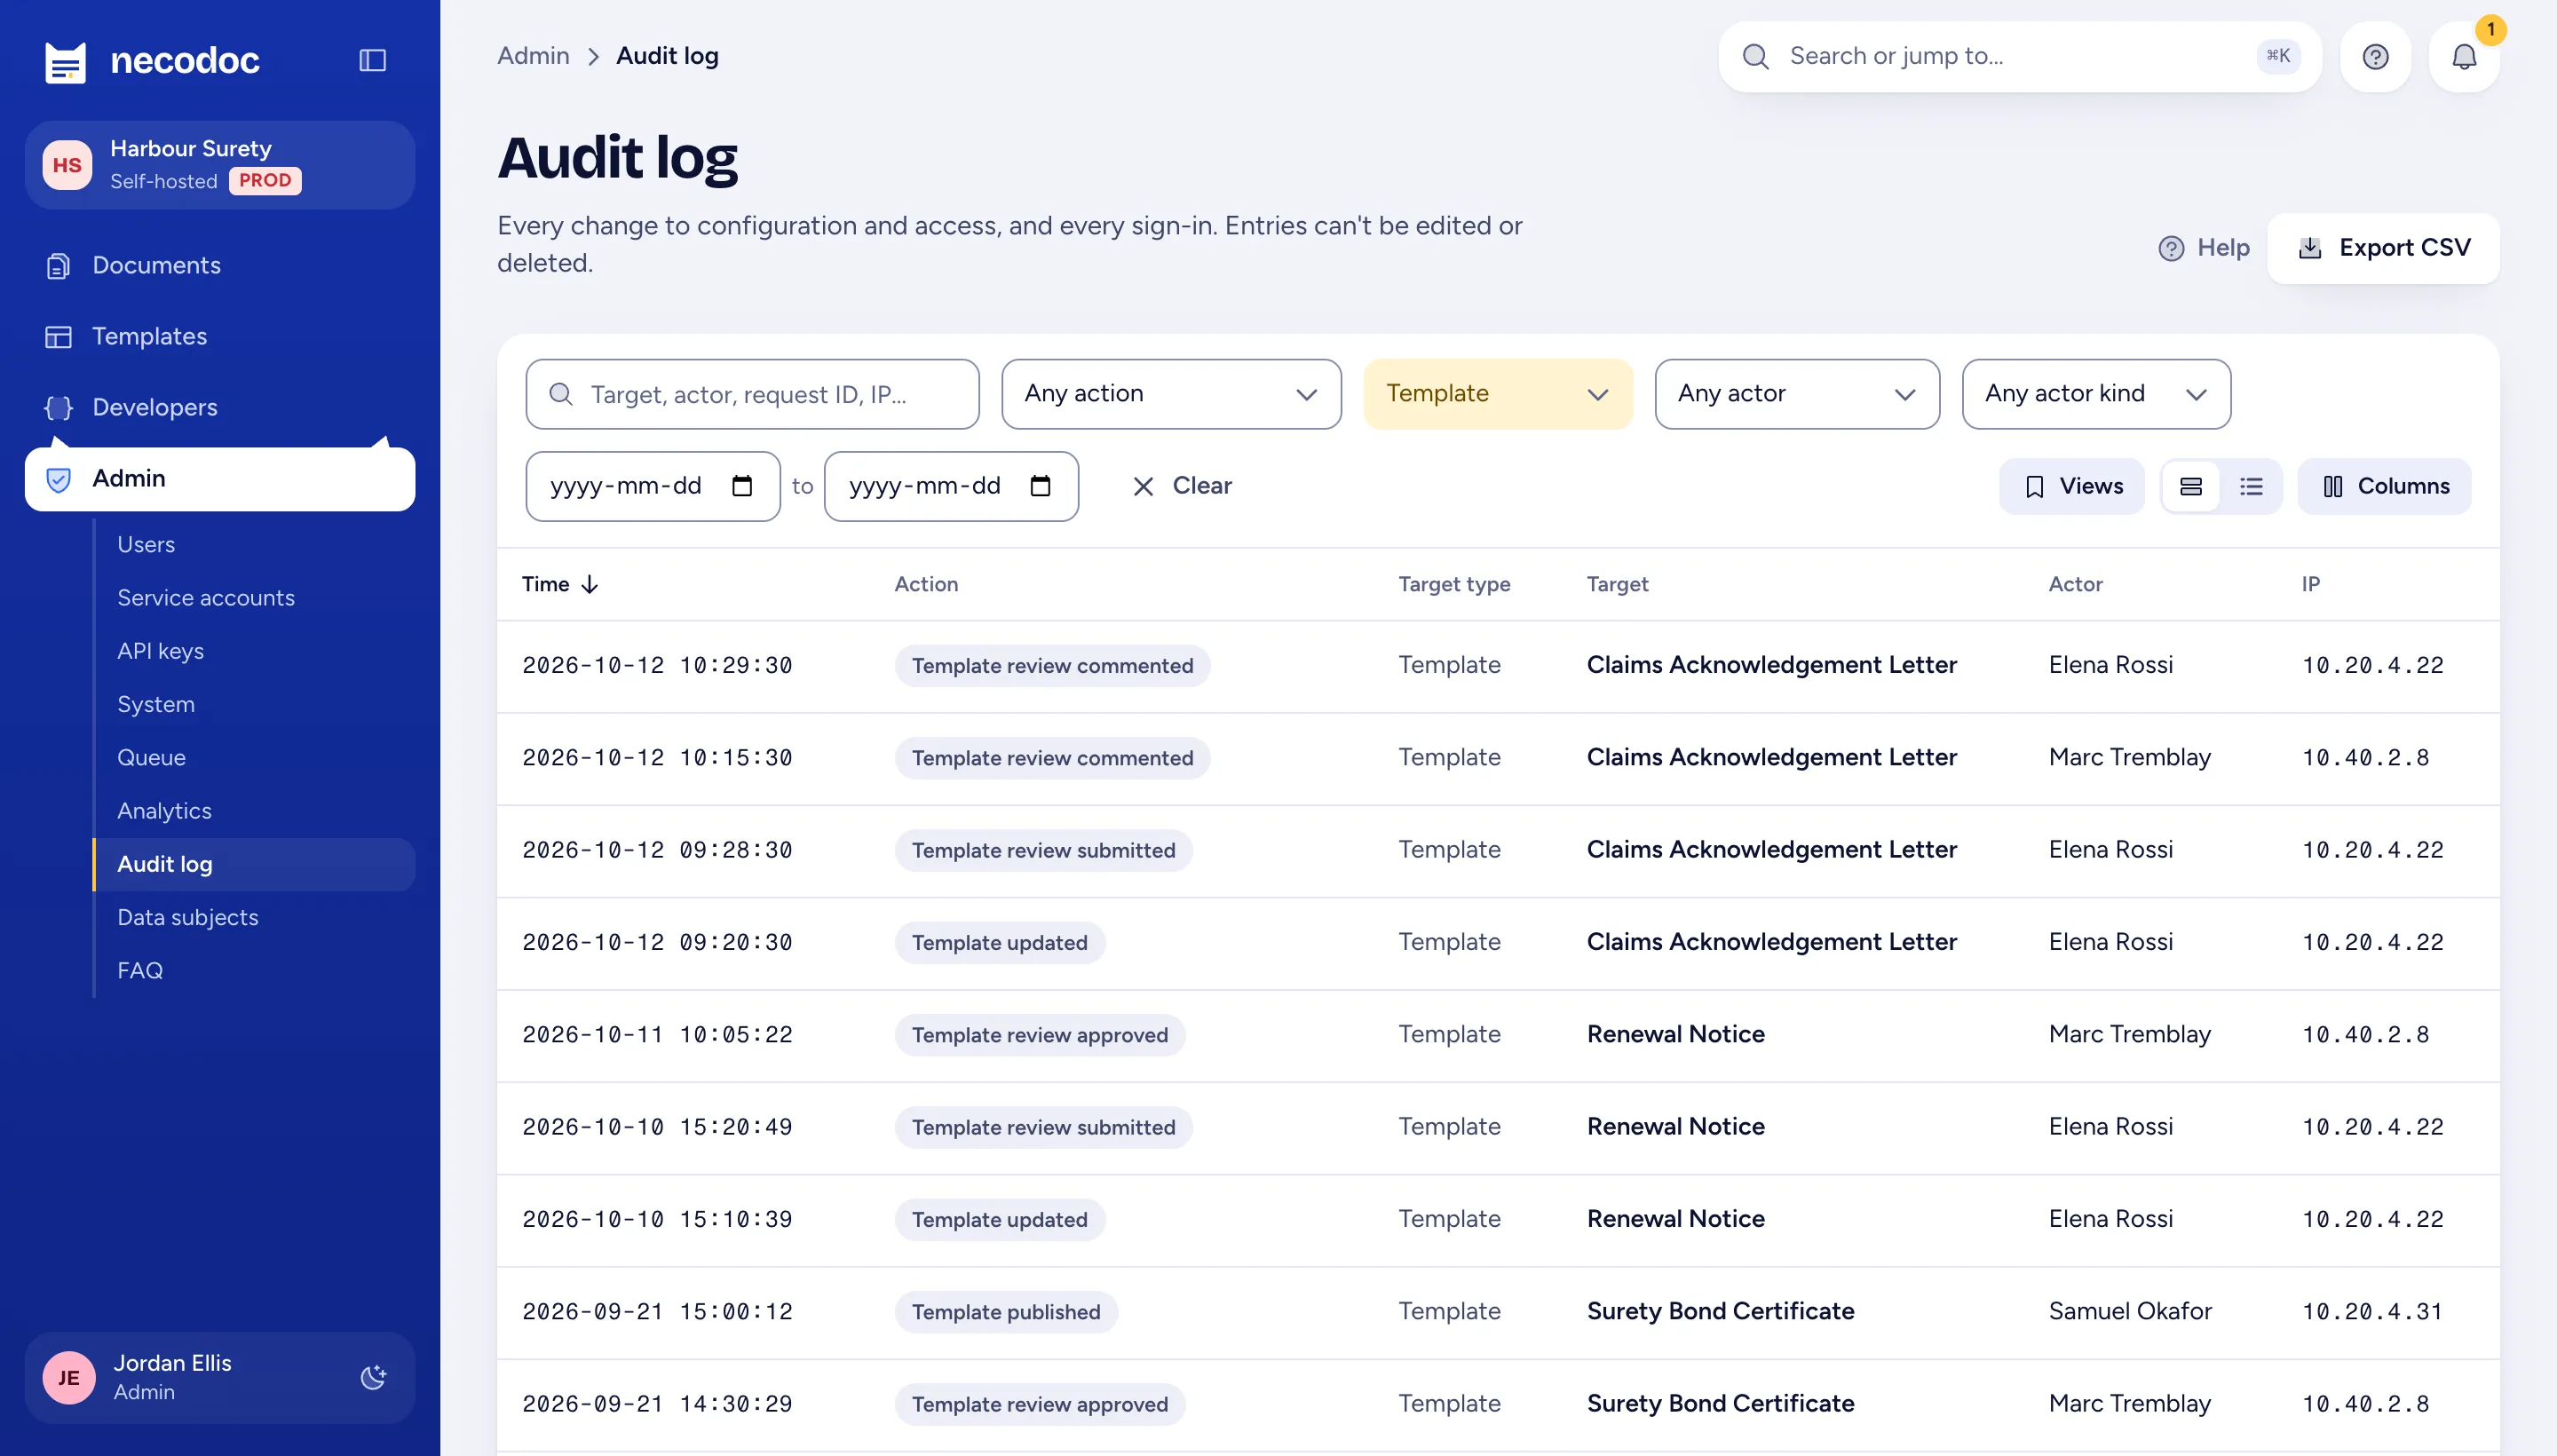
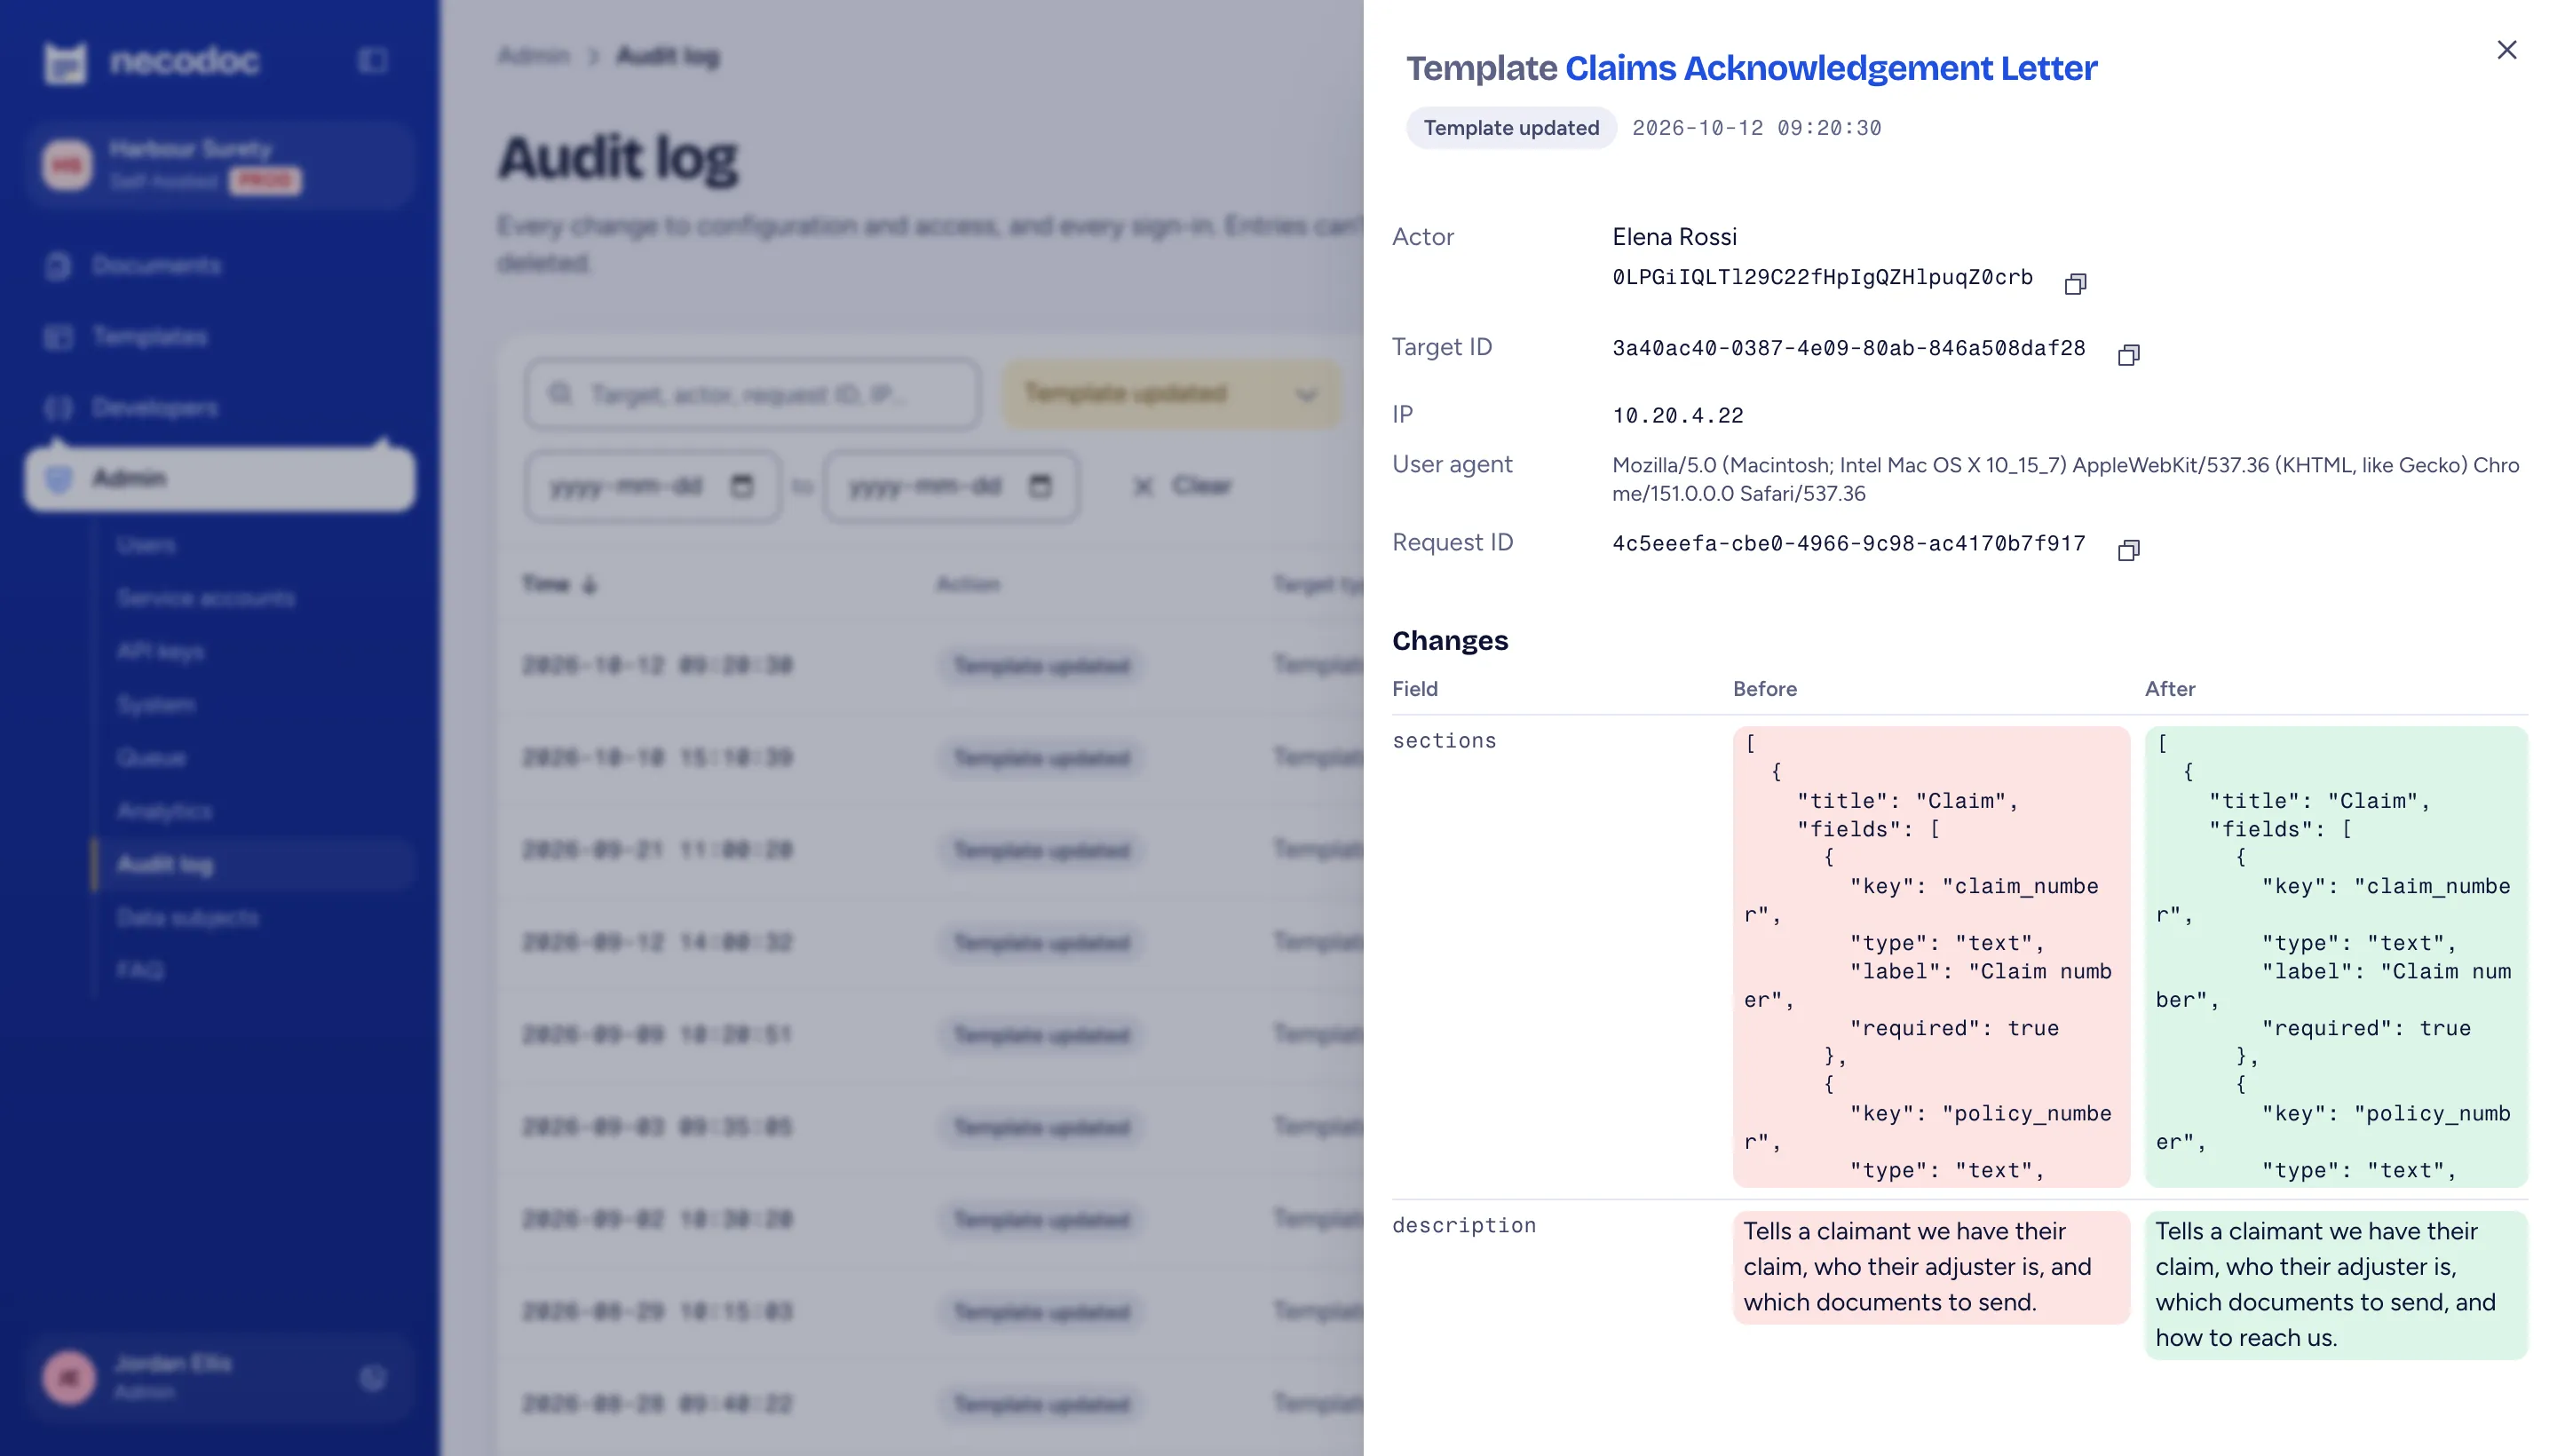
| Audit log | Every configuration and access change, sign-ins including failures, impersonation and API key use, with before and after diffs. A database trigger keeps it append-only. Exports to CSV. | Audit log |
| Generation log | Every PDF with its input, output, template version, caller and a timing breakdown; re-runnable against the exact version. | Generation log |
| Operational logs | JSON logs, Prometheus metrics and OpenTelemetry traces, with one request id end to end. Logs and traces never carry field values. | Observability |
| Change control and output |
| Versioning | Each template has one working draft. Published versions are numbered and can't change. Publishing needs its own permission. | Publishing |
| Review gate | When an admin requires it, only an approved, unchanged draft can be published. | Review |
| Regression tests | Named test cases with assertions, and a page-by-page visual and text diff against the published version. | Test cases |
| Output integrity | PDF/A-2b or 2u, PDF/UA-1, and PAdES B-B or B-T certification with your certificate. Each generation records the profiles it applied. | Archival output |
| Privacy and vendor risk |
| Sensitive fields | Fields marked sensitive are masked in audit diffs and in other people's log entries. | Personal data |
| Erasure | An admin finds everything stored about a data subject and erases it. necodoc writes an erasure report. | Personal data |
| Exit | MIT source, standard Postgres, PDFs in your storage, templates as data. No vendor holds your data. | Licence |